why don’t you fix the vuln instead of posting here
1)I am not the one who created it
2)due to certain issues irl (which is in fact confidential) I have temporarily lost access to my laptop and therefore I cannot be able to do anything for a while
3)I am a mere beginner front end dev who is struggling with JavaScript so my skills are currently limited when it comes to such complex things
So no matter how will you look at it, it is physically impossible (just for now at least) to fix the whole thing, if I could do it, then I would do it with pleasure.
Edit: forgot to add, to be brutally honest, I started working in a shop (still an intern yet, but I will do my best to finish the internship successfully), so I have to work for many hours and after work I get tired, so I don’t have much time nowadays anyway 
And we’re back for another round! In the last few hours two more exploits have been found in the server:
Targeted DoS exploit
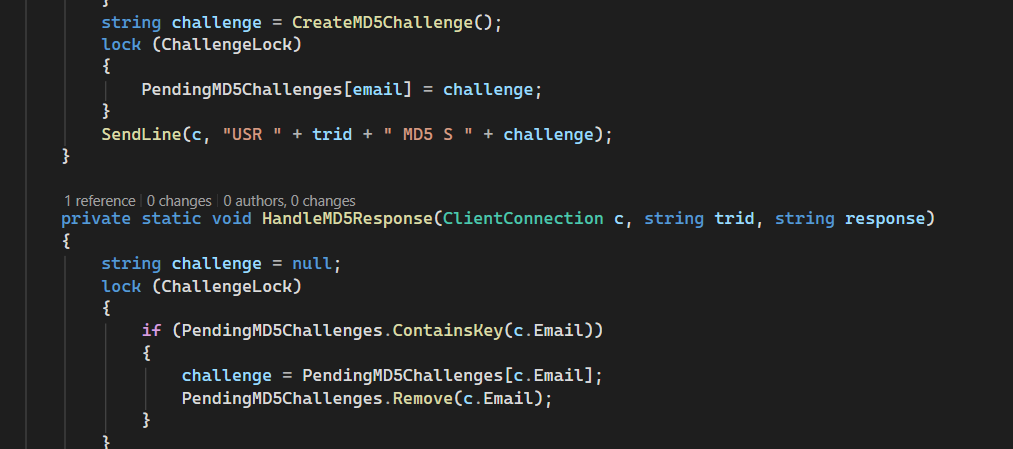
The first exploit found allows anyone to prevent a specific user from being able to sign-on to the service. This is achieved by brute-forcing MD5 login attempts, as the PendingMD5Challenges Dictionary is keyed by E-Mail, so by being racing the login you can just prevent someone from logging in.
Server Crashing Exploit
This one is way more fun and stupid. The handler responsible for MSG allows allocations of 16mb per message and under the right cirumstances, this memory is never freed. Additionally, the server is set to compile as a 32-bit Application meaning that you can really easily crash the server in a matter of minutes, if not even seconds.
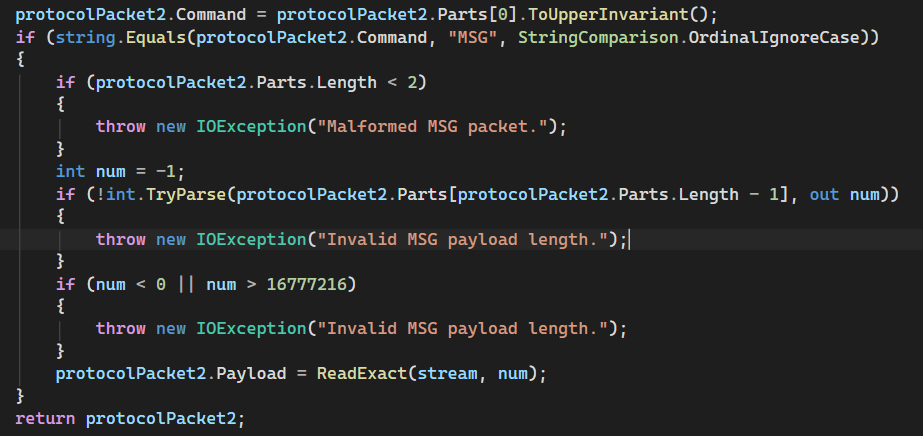
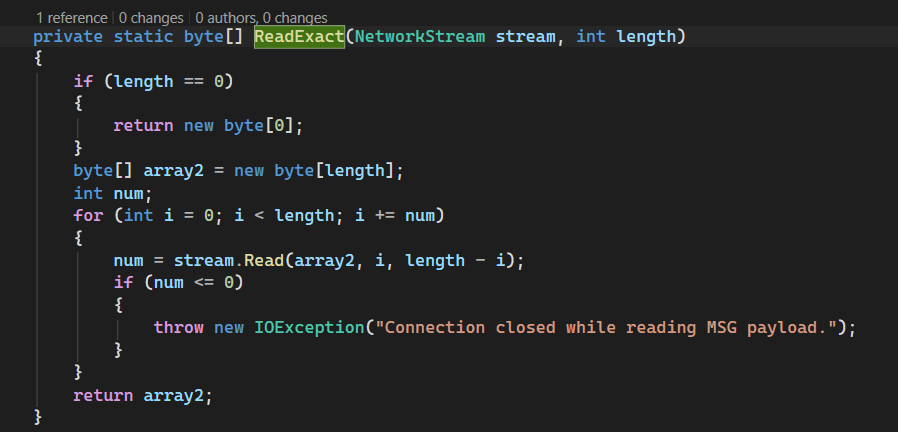
This is beyond stupid this is so much larger then any MSG object you could ever receive.
Bonus Discoveries
So fun fact, whilst implementing the TWN auth bypass, it turns out that this server has incomplete MSNP8 code and it will never correctly authenticate a legit client, meaning you can only ever sign-on with the exploit. What makes it worse is that it also never sends presence commands and SYN messages are out of sync with their TrID so the client will either hang or throw a service unavailable error, meaning you have to fake presence to the client for sign-on to complete.
Additionally, it should be possible to crash the server with bogus XFR requests, however the server runs out of XFR connections available before we actually get there.
Also, you never registered reconnected.live, so we did it for you :)) http://reconnected.live
Here’s the source code to the new exploits along with a cleaned-up C# version of the decompiled code (the original is in VB.NET but C# is much more pleasant to work with)
I urge you to never run a public service like this again with security holes so large that I can fit a forklift through it, you’re doing a disservice to yourself and your users that you put at risk doing this bullshit.
Props to the Discord oomfs that discovered both of these exploits <3 /p
3 Likes
I guess just for now people would have to stick with Google Talk and QIP until the whole thing won’t be fixed, well, I appreciate everyone’s concerns and constructive criticism, all of that info should also be an important lesson in order to make our project much better and more interesting.
Damn it. I have to rewrite the whole thing.
I used ChatGPT not opencode.
It’s of my recommendation that you never try and run a public service like this in any capacity, until you learn the skills to actually understand what you’re doing. You are doing a disservice to yourself for relying on AI to do everything for you instead of learning the proper skills, and you’re doing a disservice to your userbase by allowing them to use a service long before it’s even remotely ready to be used, littered with security holes, AI hallucinations about how MSNP works, the most important feature of an IM client being missing (that being.. IMs) etc
As I already iterated, vibe coding and blindly trusting the output where there’s clearly very glaring issues is extremely irresponsible at best. Grossly incompetent to the level of illegality at worst. I’ve seen less bad issues create massive legal trouble for other groups.
You are handling the personal information of other people. There are standards and laws you have to follow, and I can tell you right now that this ain’t up to par.
The same goes for songoku. You shouldn’t act as a spokesperson for a project that you have no idea the inner workings of, is pretty much entirely outsourced, and the only thing you’ve really done is slap the name of your own project on it.
The level of competence exhibited by Project Reconnected that I’ve witnessed is nothing that has any buisness handling the personal data of other users.
3 Likes
not what I said but there’s the confirmation that the server was vibecoded :))
Yeah, you’re right. Well that was the exe version. I switched to Python. That repo names is not funny.
storing plaintext password also isnt funny 
3 Likes
Changing the language the server uses isn’t going to fix logical bugs, unless you’re taking the findings here seriously.
6 Likes
Anyways! Let’s all calm down. No need to get mad over AI. of course it is AI.
This is implying they didn’t switch to python just to GPT “patch” everything. I suspect it’s going to generate code “better” than it did with Visual Basic.NET.
To be honest, I don’t know what GPT model you use(d) but it is allergic to writing valid MSNP commands.
Which is funny, because last time someone tried to do this, ChatGPT generated an answer that said a place with cleaner documentation.
Maybe I’m being disingenuous here, but maybe you want to try the where to find msnp documentation question first.
1 Like
1st: I used the standard ChatGPT model
2nd: To make MSN server to be perfect as possible, I make the GPT search the web for documentation including NINA Wiki and cooks up the Python code
After many attempts, it worked.
I am very much on board with HIDEN here.
These aren’t just small “oopsies”. These are issues that are genuinely so critical and obvious that I have no clue how they were never caught by anyone, not even the AI. And changing the programming language without changing the fundamental programming habits (vibe coding, anyone?) that led to this disaster in the first place is not going to do much.
I’ve seen a lot of BasicallyMachine’s work down the grapevine and, at this point, I’d go so far as to say that I would not trust any service with their name attached to it. The amount of “security nightmare” level projects I’ve seen from them is genuinely too much to count. It’s pretty much a common denominator.
We have to remember. When a user signs up to your service, they are entrusting you with their data. And there are very real, legal consequences for making mistakes in this area, that could fall back on Project Reconnected. (Yes, songoku, even if you didn’t develop the server, if you have a leadership role you could probably be held legally liable for this kind of fuckup) (this is not legal advice I’m not a lawyer)
This is a level of security incompetency I haven’t seen in the OIC since Phoenix AIM all the way back in 2021. And even then I think Phoenix might’ve genuinely had better security than this.
At this point, this is gonna end up being slide deck material on how not to ever run a service and store user data ever, smh
3 Likes
Yeah, so stop completely relying on it and learn the skills for yourself, instead of putting potentially hundreds of user’s data at risk. This isn’t something we should “calm down” about.
Switching languages and feeding it documentation (which by the way there are quite a few major issues/incompletions with the NINA wiki’s MSNP pages - which is mostly the blame of MSNPiki) does not fix the core issue that led to this occuring in the first place. Blindly vibe coding and trusting the AI’s output without attempting to understand what it’s doing. A similar sitauation is bound to occur.
I’m not sure where you live, but in the EU, under the GDPR (which every online service has to follow if they want to be accesible in the EU, even if the creators aren’t from the EU), you could be fined up to a maxmium of €20m, though realistcally it will be much lower as this isn’t a corporation, it will still be a lot of money. More in the thousands of Euros range.
This stuff is taken very very seriously.
Project Reconneceted as a whole needs to dissolve, have a hard reset, completely new leadership, whatever. Whatever the case is, the current team is not competent enough to provide a functional, secure service. I haven’t even gotten to the Google Talk/QIP server yet but that’s it’s own can of worms of What The Fuck.
4 Likes
- I have already told BasicallyMachine to not use AI few minutes ago
2)of course you cannot access Google Talk’s source code where everything is hosted via VPS (and no, not one of those free VPS which could be insecure af),even emails along with passwords are encrypted and the whole thing is closed source (because the dev behind it doesn’t likes to release and share source codes publicly, well, not surprised)
3)well, since BasicallyMachine created a new source code by using Python, I will make sure that he won’t make it go online ASAP, we might need a cyber security expert who could just dig in and tell us what could be wrong with the new code so that we could fix those issues too
4)about using AI, soon we will start the development on a new project which has codename “Aurora” (and no, we have no plans of revealing what it is, too early), that project will be developed without any AI models so I hope that once it will come out, I hope that you will be more impressed because it is something so cool that ignoring it would be a mistake.
About screwing up, you have some points, but about screwing up and receiving actual lawsuits, I have my own lawyer (not joking, really) who is ready to help me anytime, however, I will make sure that we won’t end up like Phoenix, now that would be an actual disaster and a big wound on our project’s reputation, so HIDEN did the right thing by uploading some evidences about the insecurity, that was the first indirect hint which was understood easily.
Edit: guys, if you saw any mistakes in the message, then pls don’t start scolding me separately about it, I hate my phone’s keyboard